Latest Security News

Week of Sun, Oct 18 – Sat, Oct 24, 2026 · 306 stories · Updated Thu, Oct 22, 2026 at 5:51 PM

Thursday, October 22

r/cybersecurity
Is it possible to consolidate the whole security program
r/cybersecurity4:52 PM

I’ve been going through this study by PaloAlto and IBM which coins an idea of “Platformization” which consolidates the whole Cybersecurity program under a same platform where dozens of security tools feeds, bridging the silos. https://www.ibm.com/thought-leadership/institute-business-value/en-us/report/unified-cybersecurity-platform is it really possible to build a true security platform? is…


Dark Reading
What We Missed: Feds Lasso Texas Laptop Farms
Dark Reading3:33 PM

In this video, Dark Reading editors discuss some of the news they didn't get a chance to cover, from busting up North Korea's stateside infrastructure in "Operation Lonestar Justice" to Staples' gift card bonanza.

The Hacker News
Arista Warns of Critical VeloCloud SQL Injection Zero-Day Exploited in Attacks
The Hacker News2:05 PM

Attackers are exploiting a zero-day SQL injection flaw in Arista's VeloCloud Orchestrator (VCO), the central management system for VeloCloud SD-WAN networks, the company said in an advisory on October 22. The flaw lets anyone who can log in to the orchestrator, even with a read-only customer account, gain operator privileges, the top level of control over it. For

r/cybersecurity
Unvetted AI agents are accessing U.S. bank accounts
r/cybersecurity1:51 PM

Major U.S. banks are detecting unauthorized third-party AI agents operating inside customer accounts, with some agents attempting to take actions that appear to be independent of user instructions, sources tell Axios. Banks including Morgan Stanley, Bank of America, JPMorgan, Wells Fargo, and others are racing to contain agent risks. Some are aware of unauthorized access, people familiar with the…

The Hacker News
eMudhra to Exit Global SSL/TLS Business After 8 Intermediate CA Keys Found Easily Guessable
The Hacker News1:12 PM

eMudhra, an Indian certificate authority (CA), will withdraw from its global SSL/TLS certificate business, its board decided on Thursday. The decision came five days after a researcher reported recovering the private keys of eight of its intermediate CA certificates. eMudhra said it will replace affected customers' certificates with free ones from partners, though its

r/cybersecurity
PHP2Shell: the leaked PHP RCE everyone is staging and no one has landed (yet)
r/cybersecurity12:50 PM

The php2shell leak (CVE-2026-109618 / 109619, CVSS 9.2) had everyone scrambling. We mapped the exposure (hundreds of thousands of PHP hosts, mostly on end-of-life versions) and went looking at what attackers are doing with it. Short version: lots of staging and scanning, no confirmed compromise anywhere, and no public exploit that actually works on modern systems yet. If you run PHP, patch to…

The Hacker News
ThreatsDay: AI Secrets Leak, PingCAP Source Theft, Signal Hang-Up Flaw, Laravel Auth Bypass + 21 More
The Hacker News12:45 PM

This week has already been rough for cybersecurity. Critical PHP and GitLab RCE flaws, serious Linux security bugs, compromised eMudhra certificates, a Node.js RCE flaw, a hacked LiteLLM release, and hundreds of hijacked Tor relays. That's a lot to deal with in just a few days. And the week isn't even over yet. But those big headlines are only half the story. Stolen passwords, exposed

The Hacker News
Two CVSS 9.0 Linux KSMBD RCE Flaws Disclosed on Public Mailing Lists Before Kernel Fixes
The Hacker News12:01 PM

Linux servers running KSMBD, the kernel's built-in SMB server, are exposed to two publicly reported remote code execution flaws rated 9.0 by Trend Micro's Zero Day Initiative, with no fix yet in the mainline kernel. One of them, ZDI-CAN-33774, can be triggered before any network authentication. The other, ZDI-CAN-33549, requires the SMB Direct transport and an RDMA-capable network

The Hacker News
Meta Ordered to Pay $25 Billion After Court Finds 43 Million Privacy Violations
The Hacker News11:12 AM

Social media giant Meta was ordered to pay 25 billion in penalties by a New Mexico court on Wednesday as part of a data privacy lawsuit that sprang from the company's Cambridge Analytica data scandal, which came to light in 2018. According to multiple reports from the Associated Press, the New York Times, Reuters, and the Wall Street Journal, state District Court Judge Francis J. Mathew called

Cyber Security News
Gcore Makes Enterprise Security Bundle Free for Public Agencies Until End of the Year
Cyber Security News11:12 AM

Contern, Luxembourg, October 22nd, 2026, CyberNewswire Gcore is offering its WAAP Enterprise plan free of charge to any government body or public agency until December 31, 2026. The offer follows the php2shell vulnerabilities that forced public websites offline across Europe earlier this week. Gcore WAAP blocks the php2shell attack path (CVE-2026-109618 and CVE-2026-109619) by default […] The…

Cyber Security News
Major U.S. Banks Detect Unauthorized AI Agents Operating Inside Customer Accounts
Cyber Security News10:23 AM

Major U.S. banks are detecting third-party AI agents inside customer accounts, raising concerns that automated tools could act beyond the instructions customers give them. Some agents have contacted call centers or appeared to attempt independent actions, according to an Axios report published October 22, citing people familiar with the matter. Morgan Stanley, Bank of America, […] The post Major…

Cyber Security News
eMudhra Exits Global SSL/TLS Certificate Business Following the Vulnerability Disclosure
Cyber Security News9:52 AM

eMudhra Limited has announced it is exiting the global SSL/TLS certificate business after disclosing weak private keys in eight intermediate certificate authority certificates. The October 22, 2026, decision follows emergency browser protections and growing questions about the company’s certificate issuance controls. eMudhra said its other digital trust services remain unaffected. In its official…

Cyber Security News
Claude Security Now Scans Repositories Continuously to Find Flaws and Track Fixes
Cyber Security News9:40 AM

Anthropic has updated Claude Security so it can keep checking connected code repositories as they change, rather than waiting for a person to start each scan. The service also tracks reported vulnerabilities after developers make changes, marks them fixed when a correction is detected, and reopens them if they return. The updated product is in […] The post Claude Security Now Scans Repositories…
Cyber Security News
A New Extortion Gang Is Naming Companies on the Dark Web and Counting Down to Data Leaks
Cyber Security News9:40 AM

ScarlettGroup, a newly observed cyber extortion gang, is naming companies on a dark web leak site and using countdown timers to threaten the release of allegedly stolen data. The operation puts public pressure on organizations before their breach claims have been independently verified. The group began appearing in threat monitoring records around September 2026 and […] The post A New Extortion…

Cyber Security News
Hackers Were Targeting Critical PHP Vulnerabilities Days Before They Were Patched
Cyber Security News9:14 AM

A threat actor tried to exploit two critical PHP vulnerabilities four days before the flaws were publicly disclosed and patched, according to Amazon Threat Intelligence. The activity began on October 17, 2026, while the vulnerabilities were still under coordinated disclosure. The flaws, tracked as CVE-2026-109618 and CVE-2026-109619 and known together as PHP2Shell, can allow remote […] The post…

BleepingComputer
Machine speed attacks require machine speed detection and response
BleepingComputer9:02 AM

Attackers can steal credentials and begin exfiltrating data within minutes, often before security teams can respond. Exaforce examines real-world attacks involving stolen GitHub tokens, malicious AI installers, and MFA phishing, explaining why faster detection and automated containment are critical. [...]

The Hacker News
INTERPOL Arrests 1,462 Suspects, Disrupts 10,909 Cybercrime Networks in Global Crackdown
The Hacker News8:38 AM

INTERPOL on Thursday announced that a coordinated law enforcement action has disrupted 10,909 malicious networks and recovered more than $105 million in illicit funds. In tandem, the effort saw law enforcement agencies from 21 countries arrest 1,462 suspects. Codenamed Operation Serengeti III, the cybercrime crackdown took place between June 29 and August 31, 2026. "Authorities identified

Schneier on Security
New Serious PHP Vulnerabilities Released and Patched
Schneier on Security8:26 AM

PHP maintainers have released fixes for two critical vulnerabilities: PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 fix two critical vulnerabilities that can allow unauthenticated remote code execution. All PHP users are strongly encouraged to update immediately. Who is at risk: all PHP installations serving web requests, including PHP-FPM, Apache with mod_php, php-cgi, FrankenPHP and LiteSpeed. We…

Cyber Security News
Hackers Planted Malware on Japanese Cloud Servers, Forcing the Provider to Shut Down Its Service
Cyber Security News8:05 AM

Hackers planted malware in customer server environments at Japan’s Onamae.com Desktop Cloud, prompting the provider to begin shutting down servers across every service plan. The company listed 26,739 servers as potentially affected, raising concerns about stored data and login details. That figure describes the possible scope, not a confirmed count of infected systems. The provider […] The post…

Cyber Security News
North Korean Hackers Use Post-Quantum Encryption to Hide New Malware From Security Tools
Cyber Security News7:38 AM

North Korean-linked Lazarus hackers are using post-quantum cryptography in a malware delivery chain designed to conceal later-stage payloads from security tools. The technique appeared in Operation FlashHole, a campaign targeting organizations in South Korea. Instead of relying on encryption alone to hide files on disk, the malware uses a modern key-establishment method to protect payloads […]…

Cyber Security News
A Hacker Tried to Turn an AI Chatbot Into a Tool for Attacking Other Servers
Cyber Security News7:15 AM

An exposed artificial intelligence platform can give an intruder more than a place to send messages. If it connects to stored credentials, company data, or network tools, the platform may also provide a route toward those resources. A recent honeypot investigation shows how an attacker tried to use an AI agent to study real infrastructure […] The post A Hacker Tried to Turn an AI Chatbot Into a…

The Hacker News
The AI Agent Nobody Owns: Watch Expert Webinar On Your Newest Insider Threat
The Hacker News6:45 AM

Right now, there is probably an AI agent running on a laptop somewhere in your network. It stores API keys and database passwords, can access your internal systems, and works without anyone watching. Nobody reviewed its access. Nobody owns it. If an employee had that much reach with that little oversight, you would call it an insider risk. So why do we still call the agent a productivity tool?

The Hacker News
Railway Says Intruder May Have Accessed Customer Secrets, Urges Credential Rotation
The Hacker News6:15 AM

Platform-as-a-Service (PaaS) provider Railway on Wednesday disclosed "anomalous activity" related to systems that store customer environment variables. Upon further investigation, the company found that an unauthorized third party may have gained access to encrypted environment variables, and, in some cases, obtained the decrypted contents. The impact, it said, is limited to a "subset of users,

Cyber Security News
New Android Malware Replaces Legitimate Banking Apps With Malicious Copies to Bypass Security Checks
Cyber Security News6:13 AM

A newly identified Android banking Trojan called Hirudo takes an unusual route to financial fraud: it tries to remove a victim’s genuine banking app and install a modified copy in its place. The replacement keeps the bank app’s name and version, but contains extra code designed to interfere with security checks. Instead of relying only […] The post New Android Malware Replaces Legitimate Banking…

The Hacker News
OpenCode Flaw Lets Malicious MCP Servers Execute Code During Sign-In on Windows and WSL
The Hacker News5:44 AM

A flaw in the OpenCode AI coding agent allowed a malicious or hijacked MCP server to run code on a developer's Windows or WSL machine when the developer signed in. OpenCode connects to MCP (Model Context Protocol) servers to add outside tools, and such code would run with the developer's own access. Anomaly, the company behind OpenCode, fixed the flaw in version 1.18.33 on September

Cyber Security News
Top 10 Best Secure File Sharing Platforms in 2026 [Ranked & Scored]
Cyber Security News5:16 AM

Users share files the easiest way available your only real choice is whether the easiest way is also the governed one. The 2026 secure-sharing shortlist is judged on that bargain: consumer-grade usability on top of enterprise controls (classification-aware policy, external-access governance, audit that survives a regulator), because any platform users route around is security theater […] The post…

Cyber Security News
Atlassian Releases Massive Security Update Addressing 176 Flaw Entries in Jira and Confluence
Cyber Security News5:12 AM

Atlassian has released its October 2026 security bulletin, covering 176 flaw entries across products including Jira, Confluence, Bamboo, Bitbucket, and Crowd. Published on October 20, the update lists 162 high-severity entries and 14 critical-severity third-party entries. Atlassian says it included fixes in product versions released last month and urges customers to install a suitable fixed […]…

Cyber Security News
Top 10 Best Enterprise DRM & Information Rights Management Solutions in 2026 [Ranked & Scored]
Cyber Security News4:55 AM

Perimeters don’t follow files. The deal model emailed to a counterparty, the design doc shared with a contractor, the board pack synced to a trustee’s tablet enterprise DRM (information rights management) keeps policy attached to the document itself: who can open, edit, print, screenshot, and until when, revocable after the file is long gone. We […] The post Top 10 Best Enterprise DRM &…

r/cybersecurity
Checking in
r/cybersecurity4:51 AM

The internet is a dumpster fire right now, how is everyone holding up? The past 48 hours have just been insane, getting hit with absolutely everything all at once. I work with vulns and all I can say is…yikes. Good luck these next few days/weeks, hang in there. Edit for clarification: I mean emotional/stress wise.

Cyber Security News
Fortinet Urges Customers to Patch Critical Flaws Affecting FortiOS, FortiManager, and FortiAnalyzer
Cyber Security News4:18 AM

Fortinet has urged customers to prioritize security updates for FortiOS, FortiManager, and FortiAnalyzer scheduled for October 22, 2026. The coordinated release addresses critical and high-severity vulnerabilities, including flaws found through AI-assisted security testing. The company said customers should address internet-facing devices first. In an October 21 announcement, Fortinet Chief…

Security Magazine
Are You the Insider Threat?
Security Magazine4:00 AM

A conference invitation can be easy to justify: new ideas, contacts, technology, and professional development.

Cyber Security News
Samsung and Vizio Smart TVs Still Send Tracking-Like Traffic After Users Turn It Off
Cyber Security News3:40 AM

Samsung and Vizio smart TVs kept sending traffic consistent with automatic content recognition (ACR) even after researchers turned off the feature in the privacy settings. The findings raise questions about whether smart TV privacy controls stop viewing-related data flows, while also clarifying an important limit. Encrypted traffic prevented researchers from confirming exactly what these devices…

Cyber Security News
Hackers Actively Exploiting Siemens Software Center Flaw in ClickFix Malware Attacks
Cyber Security News3:29 AM

Hackers are exploiting a DLL side-loading flaw in Siemens Software Center to run malware through a trusted, signed application. Tracked as CVE-2026-110936, the weakness affects versions before 4.0.9.8. Siemens has confirmed active exploitation and released a fix, and existing installations will receive the update the next time the application starts. Siemens published security advisory SSA-580366…

The Hacker News
LiteLLM Suspects GitHub Token Leak in AI Gateway Logs Behind Malicious Package Release
The Hacker News3:28 AM

LiteLLM on Wednesday disclosed that threat actors compromised "multiple independent security controls" to push a malicious version of the Python package containing a credential stealer and a backdoor. On October 21, 2026, LiteLLM's release pipeline was compromised to push 1.107.0 to the Docker Hub registry and the Python Package Index (PyPI) repository. The incident took place around 4:00 a.m.

BleepingComputer
Authorities disrupt nearly 11,000 cybercrime networks in Africa
BleepingComputer3:27 AM

Law enforcement agencies have disrupted nearly 11,000 cybercriminal networks and arrested more than 1,400 people in Operation Serengeti III, which targeted business email compromise, ransomware, and online scams. [...]

Cyber Security News
Critical Signal Vulnerability Could Keep Your Mic and Camera Live Even After Hang Up
Cyber Security News3:26 AM

A critical vulnerability in Signal’s calling library could allow a malicious call participant to keep hearing audio after another user tries to hang up. The flaw, tracked as CVE-2026-113380, affects RingRTC versions before 2.72.0 and carries a CVSS severity score of 9.3. Video could also remain active, although the published description does not confirm that […] The post Critical Signal…

Cyber Security News
Hackers Are Using Real Dell and Staples Emails to Make Their Scams Look Legitimate
Cyber Security News3:04 AM

Hackers are abusing genuine Dell and Staples order emails to make fake purchase alerts look credible. Instead of sending a forged message, they place scam instructions inside order details that trusted retail systems deliver, pushing recipients toward phone numbers controlled by the attackers. The emails describe expensive purchases that recipients may not recognize. Their aim […] The post…

The Hacker News
Node.js Brotli Decoder Bug Could Allow Remote Code Execution in All Supported Versions
The Hacker News2:47 AM

Node.js released security updates on October 21 for its three supported release lines, 22.x, 24.x and 26.x, fixing 10 flaws. The most serious is a bug in the Brotli decompression code that Node.js bundles, which the project says can allow remote code execution, meaning an attacker could run code of their choosing on the affected system. Each supported line has one fixed version:

Cyber Security News
Hackers Used Claude and Grok to Automate Cyberattacks on Over 400 Banks and Financial Firms
Cyber Security News2:24 AM

A cybercrime group used artificial intelligence (AI) agents to coordinate attacks against more than 400 banks, payment providers and other financial organizations across Latin America, according to a report by cybersecurity company Straiker. The group, known as CyberCartel, reportedly used AI models from Anthropic, xAI and Moonshot AI to help plan and carry out parts […] The post Hackers Used…

The Hacker News
New QPACK Flaws Can Crash HTTP/3 Servers, Trigger Up to 4,000-Fold Memory Amplification
The Hacker News1:38 AM

A remote attacker who has not logged in can crash many HTTP/3 web servers with a single connection, security firm FoxIO disclosed, releasing working proof-of-concept code. By sending a small batch of compressed HTTP headers that expands in memory to a much larger set, the attacker can force the server to use thousands of times more memory than it received, enough to run a default server

The Hacker News
Someone Tried to Exploit PHP2Shell 4 Days Before the Vulnerabilities Were Publicly Disclosed
The Hacker News1:34 AM

Amazon's Threat Intelligence team on Wednesday said it detected an attempt to exploit the newly disclosed PHP2Shell vulnerabilities on October 17, 2026, against its MadPot honeypot service, as the flaws come under broad exploitation in the wild following the release of the patches. "The exploit attempt originated from an IP address associated with a commercial anonymization network," CJ Moses,

Cyber Security News
China-Linked Hackers Use ARTEX AI to Target 2,250 Microsoft 365 Tenants After ConnectWise Breach
Cyber Security News12:25 AM

China-state-aligned hackers used ARTEX, an AI-powered penetration-testing framework, to attempt access to more than 2,250 Microsoft 365 tenants following the ConnectWise Cloud Backup breach. Microsoft attributed the attack to Storm-0940 and reported 2,900 sign-in attempts per minute, leaving security teams little time to investigate and block access. The attackers abused stolen application…

Wednesday, October 21

The Hacker News
China-Linked Hackers Use ARTEX AI Agents in ConnectWise Supply Chain Attack
The Hacker News11:21 PM

Microsoft on Wednesday disclosed that a China state-aligned actor dubbed Storm-0940 was behind the recent supply chain compromise of the ConnectWise Cloud Backup application. During the incident, Storm-0940 used ARTEX, a Go-based agentic AI penetration testing framework that was made closed-source in the wake of its abuse against South Korean financial institutions, to speed up scanning and

Cyber Security News
Railway Security Incident: Hackers May Have Accessed Customer Environment Variables
Cyber Security News10:04 PM

Railway has disclosed a security incident in which an unauthorized third party may have accessed customer environment variables, including some decrypted values. The cloud platform warned that the affected data could contain API keys, database passwords, and private registry credentials, and urged all customers to replace stored secrets. The company published its security disclosure on […] The…

Cyber Security News
12-Year-Old GitLab Vulnerability Allows Remote Code Execution on Self-Managed Server
Cyber Security News9:06 PM

GitLab has released urgent security updates for a critical vulnerability that could let attackers run code on self-managed servers without logging in. Tracked as CVE-2026-110264, the flaw carries the maximum CVSS score of 10.0 and affects both GitLab Community Edition and Enterprise Edition. The company published the fixes on October 21, 2026. The affected code […] The post 12-Year-Old GitLab…

Cyber Security News
GoDaddy Revoking 404,607 TLS Certificates Following Compliance Failures
Cyber Security News8:43 PM

GoDaddy launched a mass revocation of 404,607 SSL/TLS certificates after finding that issued certificates did not match its published certificate policies. The company missed its required revocation deadline, creating a second compliance issue. An updated customer notice says the incorrectly issued certificates were revoked on October 21, 2026. The incident affects certificates issued under…

r/netsec
CVE-2026-109618 and CVE-2026-109619 Are Two Directions Through the Same Pre-RINIT Window
r/netsec7:29 PM

Leak hit HN 2026-10-20 15:20Z. PHP 8.5.12 / 8.4.27 / 8.3.36 / 8.2.35 fix both CVEs. Mechanism: php_request_startup() calls php_hash_environment() (multipart parse, the session.upload_progress callback, php_session_initialize() on the process-wide BG(serialize)/BG(unserialize)) one line before zend_activate_modules() runs basic's RINIT, which is what zeroes them. CVE-2026-109618 is the exit…

The Hacker News
Critical GitLab Flaw (CVSS 10.0) Could Allow Unauthenticated RCE Across 12 Years of Releases
The Hacker News1:57 PM

GitLab released fixes on October 21 for a flaw that lets an attacker run code on a self-managed server without logging in, and it affects every version of the software going back to 7.0, released in 2014. The fix matters even for administrators who patched nine days earlier: the October 12 update covered only versions 19.2 and later, and the new fixed versions sit one patch above it, so an

The Hacker News
LiteLLM Compromised in Supply Chain Attack Delivering Credential Stealer and Backdoor
The Hacker News1:01 PM

The popular LiteLLM Python package has been compromised as part of a software supply chain attack that delivered a credential stealer and a backdoor, according to reports from SafeDep, Socket, StepSecurity, and Upwind. The compromise affects LiteLLM 1.107.0, distributed through PyPI wheels and Docker images. The Python package has since been quarantined on Python Package Index (PyPI), and the

r/cybersecurity
Today's PHP Security Release, and How We're Strengthening PHP Security — The PHP Foundation
r/cybersecurity12:06 PM

On October 21st at 07:41 UTC, more than six hours before the coordinated release, Chainguard unilaterally broke the embargo and published built images containing the fix. Like other distributors, Chainguard had received the patch in advance so its users could update the moment the vulnerabilities were disclosed. Any attacker could now study the fix in binary form while every other PHP user was…

Cyber Security News
Arrakis Security Report Finds 76% of AI Agents Are Dormant but Keep Their Credentials and Connections
Cyber Security News12:05 PM

New York, NY, USA, October 21st, 2026, CyberNewswire According to the 2026 Autonomous Agents Threat Report, published by Arrakis Security, 76% of active agents have not run in 60 days, but their credentials still work and their triggers still fire. 44% have not run in 180 days. 24% of dormant agents can be started by […] The post Arrakis Security Report Finds 76% of AI Agents Are Dormant but Keep…

Cyber Security News
The AI Adoption Blind Spot: How Fake AI Tools Put Enterprises at Risk
Cyber Security News11:53 AM

AI adoption is accelerating across enterprises, with employees increasingly relying on platforms like ChatGPT, Claude, and Microsoft Copilot for everyday work. Cybercriminals are exploiting this growing trust, distributing malicious applications disguised as legitimate AI tools to steal credentials, deliver malware, and gain access to corporate environments.  Recent research by ANY.RUN reveals…

Cyber Security News
Node.js Releases Security Updates to Fix High-Severity TLS, DNS and Brotli Vulnerabilities
Cyber Security News11:33 AM

Node.js has released security updates for its 26.x, 24.x, and 22.x branches to address ten vulnerabilities, including four high-severity flaws affecting DNS lookups, TLS certificate checks, and Brotli decompression. The supplied release details identify 26.12.1, 24.22.1, and 22.23.4 as the patched versions. The most serious potential outcome is remote code execution through the Brotli decoder…

The Hacker News
OpenAI's GPT-6 Agent Removed Safety Monitoring, Then Falsely Denied Doing So
The Hacker News11:33 AM

OpenAI has revealed that two artificial intelligence (AI) agents powered by GPT-6.1 Sol and one GPT-6 Astra weakened misalignment monitoring while making requested software changes during two internal coding tasks. The AI company said the incident took place on October 3 and 6, 2026, for Sol and Astra, respectively, as part of an internal deployment. "A GPT-6.1 Sol agent repairing an

Cyber Security News
Hackers Use AI-Powered Browsers to Hide Thousands of Fake Accounts and Bypass Security Detection
Cyber Security News10:54 AM

Cybercriminals are using AI-enabled “antidetect” browsers to manage large networks of fake online accounts while making each profile appear to come from a different person, device, or location. Check Point Research reported that these tools can help a single operator or small group run thousands of accounts across social media and other platforms, making it […] The post Hackers Use AI-Powered…

Cyber Security News
Hackers Use Gentlemen Ransomware to Disable Windows Defender and Destroy Backups
Cyber Security News10:30 AM

A ransomware operation known as The Gentlemen is using a mix of security tampering, service disruption and file encryption to make recovery harder for affected organizations. Its Windows malware can turn off Microsoft Defender’s real-time protection, add broad exclusions that reduce scanning, stop backup-related services and delete Volume Shadow Copies. These steps weaken defenses and […] The…

Krebs on Security
Widespread PHP Flaw May Cause Many Site Outages Today
Krebs on Security10:26 AM

Expect to see quite a few websites serving "404" or "Page Not Found" errors today: Nearly 70 percent of websites need to update their core software to fix a pair of vulnerabilities that allow an attacker to seize full control over affected servers. Experts say there are working exploits for the flaws, and that these critical bugs are already being exploited in the wild.

Cyber Security News
Google Upgrades Chrome With Gemini AI to Detect Fake Antivirus and Browser Update Scams
Cyber Security News10:14 AM

Google has upgraded Chrome’s Enhanced Protection mode with a more powerful Gemini AI model to detect fake antivirus alerts, browser update scams, and other deceptive websites. Announced on October 20, 2026, the changes also introduce suspicious site warnings and protection against ClickFix attacks that trick users into running malicious commands. The update expands Google’s earlier […] The post…

Cyber Security News
LiteLLM Compromised – Hackers Injected an Infostealer and RAT in the Latest 1.107.0 PyPI Release
Cyber Security News10:11 AM

LiteLLM version 1.107.0 was compromised on PyPI on October 21, 2026, spreading a credential stealer and a remote access trojan through all seven distributed wheel files. The malicious release also reached Docker images, putting developer systems, build runners, and AI services at risk. Aikido warned that anyone who installed the affected release should assume credentials […] The post LiteLLM…

r/netsec
uCreator: virtualization-based Android spyware platform targeting WeChat, Telegram and other messaging apps
r/netsec10:06 AM

uCreater (the vendor's own name for the product is YingGai ) is a commercial Android surveillance platform built around 群控 (“mass control”). Branded through packages in the com.ucreator.* namespace, it is not a single malware family but a productized framework: a VirtualApp/LSPatch engine, a library of per-application hook modules, a Redis and HTTP control plane, a cloud-phone farm for live…

Cyber Security News
China-Linked Hackers Turn Trusted Windows Applications Into Backdoors to Steal Credentials
Cyber Security News10:04 AM

China-linked hackers are using trusted Windows applications to load hidden backdoors, collect system details, and steal Active Directory credential data. The group, tracked as BRONZE SANDCASTLE, places malicious files beside legitimate software, allowing familiar programs to run attacker-controlled code without changing the original application. The campaign shows how genuine software can become…

Cyber Security News
PHP Releases Emergency Patches for PHP2Shell Flaws Threatening Millions of Web Servers
Cyber Security News9:38 AM

PHP has released emergency security updates for two critical vulnerabilities that could let unauthenticated attackers run code on vulnerable web servers. Tracked as CVE-2026-109618 and CVE-2026-109619, and collectively called PHP2Shell, the flaws affect PHP’s handling of memory during web requests. The PHP project rates both vulnerabilities 9.2 out of 10 under CVSS 4.0. Administrators should […]…

Cyber Security News
APT28 Hackers Open Secret SSH Tunnel Into NATO Country’s Naval Shipbuilder Network
Cyber Security News9:37 AM

Russian cyberespionage group APT28 used the Hookedge backdoor to reach a naval shipbuilder’s network in a NATO member state, steal login material and set up a hidden SSH tunnel. The intrusion lasted at least two months, according to a report by Symantec’s Threat Hunter Team. The report does not name the shipbuilder or the country. […] The post APT28 Hackers Open Secret SSH Tunnel Into NATO…

r/cybersecurity
I built a full-chain Chrome exploit in 6 days using only gpt-5.6-sol…Ask Me Anything!
r/cybersecurity9:09 AM

Hi Reddit! I’m Brendan Dolan-Gavitt , XBOW’s native team lead. In August, I used gpt-5.6-sol to see if I could build a full-chain exploit against Google Chrome. Six days later, we had a working chain. The exploit chained three vulnerabilities to achieve remote code execution and escape the Chrome sandbox, ultimately earning a $250,000 reward from Google’s Chrome Vulnerability Reward Program (the…

BleepingComputer
PHP ships emergency patches for critical PHP2Shell flaws
BleepingComputer9:07 AM

The PHP security team released emergency security patches for two critical remote code execution (RCE) vulnerabilities (CVE-2026-109618 and CVE-2026-109619) tracked collectively as PHP2Shell. [...]

BleepingComputer
ClickFix has never been bigger, and AI tools are its most convincing lure yet
BleepingComputer9:00 AM

ClickFix attacks are surging as cybercriminals use fake AI installers, malicious search results, and trusted chatbot platforms to trick users into executing malware. Push Security examines how these attacks evade traditional defenses and why AI tools have become increasingly effective lures. [...]

The Hacker News
PHP Issues Emergency Patches for Two Critical PHP2Shell RCE Flaws as Exploit Attempts Emerge
The Hacker News9:00 AM

PHP has released emergency updates that fix two critical flaws in the language itself, letting an attacker without an account run code on a web server. The fixes are in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, and the PHP team says only updating fully protects a server. The flaws, together called PHP2Shell, sit in the PHP runtime, not in any application, so a site is exposed even when its own

The Hacker News
Google Chrome Adds ClickFix Warnings to Stop Users From Running Malicious Commands
The Hacker News8:15 AM

Google on Tuesday said it's rolling out improved safeguards in its Chrome browser to secure users against ClickFix attacks when Enhanced Protection is enabled. ClickFix is a popular social engineering technique in which bad actors trick users into copying and pasting malicious code directly into their computer's operating system, thereby bypassing conventional security controls. As part of

The Hacker News
China-Aligned Bronze Sandcastle Abuses Sandboxie DLL Sideloading to Deploy Backdoors
The Hacker News7:05 AM

Cybersecurity researchers have disclosed details of a previously undocumented China-aligned threat cluster known as Bronze Sandcastle that has been observed targeting organizations in Asia and Africa since mid-2025. "The most distinctive technical marker for Bronze Sandcastle is its consistent use of Sandboxie DLL sideloading," Sophos security researcher Gabor Szappanos said in a post published

The Hacker News
Generative AI Is Erasing Behavioral Tells, Weakening Behavior-Only Detection, Proofpoint Reports
The Hacker News6:53 AM

Generative AI has changed what a malicious email looks like. Messages that once gave themselves away through clumsy wording, generic pretexts, and reused templates now arrive fluent, personalized, and unique to each recipient, and the behavioral signals email filters have relied on for years are fading as a result. Proofpoint shared several examples of the shift at its Protect 2026 conference.

Cyber Security News
Massive Oracle Security Update – 1295 Flaws Patched, Including Critical E-Business Suite Vulnerability
Cyber Security News6:26 AM

Oracle has released its October 2026 Critical Patch Update, delivering 1,295 new security patches across its software portfolio. Published on October 20. The update includes a maximum-severity Oracle E-Business Suite vulnerability that allows attackers without login credentials to take over an affected Workflow component through network access. The headline figure reflects security patches rather…

Cyber Security News
Fortinet FortiSIEM RCE Vulnerability Gets Public Exploit That Requires No Login
Cyber Security News6:09 AM

A public proof-of-concept exploit has been released for CVE-2026-106173, a critical vulnerability in Fortinet FortiSIEM that can let a remote attacker write files and run code without logging in. The flaw affects FortiSIEM 7.5.0. Fortinet released a fix in version 7.5.1, while version 7.6 is not affected, according to published reporting on the advisory. Fortinet […] The post Fortinet FortiSIEM…

Schneier on Security
Workshop on Economics and Information Security (WEIS) Archive
Schneier on Security6:02 AM

There’s a new archive of all the papers from twenty-five years of the Workshop on Economics and Information Security (WEIS). Really nice resource. It’s fun to reread my 2002 essay on the economics of information security.

The Hacker News
PHP2Shell: What Actually Protects You Before the 14:00 UTC PHP RCE Patch, and What Doesn't
The Hacker News5:36 AM

You cannot fully block the two critical PHP flaws called PHP2Shell before today's fix, and the one setting being passed around as a workaround is not enough on its own, the security firm that suggested it now says. PHP will release the fix at 14:00 UTC on October 21 for two flaws it rates 9.2 out of 10, and has given no workaround of its own. Until you can install it, what lowers your

The Hacker News
The Harness Is the Hard Part of Agentic Pentesting
The Hacker News5:32 AM

An AppSec team can point an AI agent running on a general-purpose model at its own web apps with little setup. Sure, the model writes the attacks. But everything that makes those attacks safe to run against production and worth acting on afterward lives in the harness around the model. The harness is where the engineering in AI pentesting sits. The Hugging Face intrusion OpenAI disclosed in July

The Hacker News
Attackers Hijacked Over 300 Tor Exit Relays to Intercept SSH Connections
The Hacker News5:30 AM

Attackers took control of more than 300 Tor exit relays in early October and used them to redirect SSH connections to servers that stole login passwords, a researcher found. Exit relays are the last hop in a Tor circuit, where traffic leaves the network for its destination. Only a password login to an SSH server made through Tor between October 1 and 5, after accepting the interception

Cyber Security News
PHP2Shell Vulnerability Gets a Public PoC Exploit for Security Testing
Cyber Security News5:15 AM

A public proof-of-concept repository shares verification tools and a lab setup to test two critical PHP vulnerabilities known as php2shell. The flaws, tracked by researchers as CVE-2026-109618 and CVE-2026-109619, are reported to affect PHP’s session.upload_progress feature and could lead to remote code execution under certain conditions. The release adds technical detail to a fast-moving…

Cyber Security News
Microsoft Offers $40,000 for Complete Azure Vulnerability Reports, Just $4,000 for Incomplete Ones
Cyber Security News4:39 AM

Microsoft has introduced a new report-assessment system across its bug bounty programs, making the evidence security researchers submit a key factor in their rewards. Under the Azure bounty program, eligible critical remote code execution and privilege escalation reports can earn $40,000 when assessed as Complete, compared with $4,000 when marked Not Complete. The change applies […] The post…

Cyber Security News
Microsoft Unveils New OneDrive Command-Line Tool to Manage Sync Deployments
Cyber Security News4:38 AM

Microsoft has introduced a new command-line tool that gives IT admins a faster way to check and manage OneDrive sync across company devices. Microsoft introduced the OneDrive Sync Client Command Line Interface (CLI) at the OneDrive + Copilot event held today. It is aimed at teams that look after large Microsoft 365 setups. The tool […] The post Microsoft Unveils New OneDrive Command-Line Tool to…

The Hacker News
Attackers Abuse UpdraftCentral Keys to Plant Backdoors on WordPress Sites
The Hacker News4:01 AM

Unknown threat actors breached TeamUpdraft's website and potentially gained unauthorized access to customers' connection keys for UpdraftCentral, UpdraftVault, and UpdraftClone, using them to backdoor WordPress sites. TeamUpdraft is the developer behind UpdraftPlus, a popular WordPress backup plugin with over four million active installations. The vendor also offers UpdraftCentral, a remote

Cyber Security News
Apache Tomcat Fixes 8 Security Flaws That Could Let Hackers Bypass Authentication
Cyber Security News3:28 AM

Apache Tomcat has fixed eight security flaws that could let attackers bypass password checks, expose data between users, and disrupt connections under specific conditions. Apache disclosed the vulnerabilities on October 20, 2026, after releasing fixes in Tomcat 11.0.27, 10.1.61, and 9.0.123. The eight issues span different release branches, so not every flaw affects every version. […] The post…

The Hacker News
U.S. Orders DeepSeek Removed From Federal Civilian Systems, Bans New Purchases
The Hacker News3:04 AM

U.S. federal civilian agencies must remove DeepSeek products from their information technology systems, along with any third-party products or services "developed using DeepSeek implementations," under a Department of Homeland Security order. They may also no longer buy information technology products or services from the Chinese AI developer or its affiliates Homeland Security Secretary

Cyber Security News
Top 10 Best File Integrity Monitoring (FIM) Tools in 2026 [Ranked & Scored]
Cyber Security News2:49 AM

Every breach eventually touches a file a dropped binary, an edited config, a replaced DLL and file integrity monitoring is the control that notices. The 2026 challenge isn’t detection, it’s signal: PCI DSS 4.x demands FIM, but a tool that pages on every patch Tuesday trains the SOC to ignore the one change that matters. […] The post Top 10 Best File Integrity Monitoring (FIM) Tools in 2026…

The Hacker News
State Bank of India Confirms Data Leak After 3,897 Customer Records Found on Dark Web
The Hacker News2:44 AM

State Bank of India has identified 3,897 customer records containing personal information in a set of about 375,000 records available on the dark web, and it does not yet know where the data came from. The state-owned bank, India's largest, said in a stock-exchange filing dated October 21 that it "has experienced an incident involving the loss of certain data." The count is

Cyber Security News
Top 10 Best Data Masking Tools in 2026 [Ranked & Scored]
Cyber Security News2:42 AM

The fastest way to leak production data is to copy it somewhere less defended and most organizations do exactly that every sprint, cloning customer records into test, analytics, and now AI-training environments with a fraction of production’s controls. Data masking closes that gap by making the copies worthless to steal while keeping them useful to […] The post Top 10 Best Data Masking Tools in…

Cyber Security News
Top 10 Best Data Privacy Management Software in 2026 [Ranked & Scored]
Cyber Security News2:35 AM

Privacy stopped being a policy problem and became a data-engineering problem: you cannot fulfill a deletion request against data you cannot find, and in 2026 more US states, deeper AI-governance rules, and shrinking DSAR deadlines punish teams still running privacy on spreadsheets. We scored ten platforms across discovery depth, DSAR automation, consent orchestration, and mid-market […] The post…

Cyber Security News
Top 10 Best Database Security & Activity Monitoring Tools in 2026 [Ranked & Scored]
Cyber Security News2:30 AM

Databases hold what attackers came for, and service accounts hold the widest keys database security decides whether either gets noticed.We scored ten options from enterprise DAM anchors to warehouse-era access layers. Imperva takes 1 for watching-plus-stopping; IBM Guardium and Satori complete the podium. Key Takeaways • 1 overall: Imperva the DAM anchor that blocks policy […] The post Top 10…

The Hacker News
CISA Orders Federal Agencies to Patch Exploited Plex2Shell, Siemens, and SiteGuard Flaws
The Hacker News2:26 AM

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday added four vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including four vulnerabilities impacting Plex Media Server that's collectively called Plex2Shell. The vulnerabilities are listed below - CVE-2026-96652 (CVSS score: 5.3) - Plex Media Server Server-Side Request Forgery (SSRF)

The Hacker News
Hackers Hid Vasilek Backdoor in VMware Tools During 2-Year Russian Healthcare Intrusion
The Hacker News1:05 AM

A Belarus-aligned hacktivist group spent nearly two years within the network of a Russian healthcare organization. According to a report published by Russian cybersecurity firm Solar, the activity has been attributed to a threat cluster dubbed Partisan Zmiy, which is also known as the Cyber Partisans. Known to be active since at least 2020, the group has a track record of striking industrial

Cyber Security News
WordPress Backup Plugin Developer Hacked to Inject Malicious Code on Installed Sites
Cyber Security News12:01 AM

TeamUpdraft, the developer behind the UpdraftPlus WordPress backup plugin, has disclosed a website breach that exposed remote management keys. Attackers used those keys to install malicious plugins on connected WordPress sites, turning a trusted management feature into a route for running harmful code. The company identified unauthorized access to teamupdraft.com during October 17–18, 2026…

Tuesday, October 20

The Hacker News
PHP2Shell: Two Unpatched Critical PHP RCE Flaws (CVSS 9.2) Trigger Emergency Security Alert
The Hacker News11:57 PM

PHP will ship an out-of-cycle security release at 14:00 UTC today, October 21, for two critical vulnerabilities that its security team has rated 9.2 on the CVSS v4.0 scale but has not described. Security researchers at watchTowr say the two flaws allow remote code execution. Only the four supported PHP branches, 8.2 through 8.5, can receive the fix, and no exploitation has been reported so far.

Cyber Security News
PHP Warns of Two Critical 9.2 Security Vulnerabilities, Urges Users to Prepare for Patches
Cyber Security News10:32 PM

The PHP security team has warned users about two critical vulnerabilities and urged administrators to prepare for an upcoming security release. Both flaws carry a CVSS v4.0 score of 9.2. Updates are scheduled for Wednesday, October 21, 2026, at 14:00 UTC, giving website owners and hosting providers a short window to prepare. In its official […] The post PHP Warns of Two Critical 9.2 Security…

BleepingComputer
Stolen UpdraftCentral keys used to backdoor WordPress sites
BleepingComputer8:01 PM

A threat actor breached TeamUpdraft's website, a developer of popular WordPress backup and security plugins, potentially compromising UpdraftCentral connection keys that can send commands to connected websites. [...]

BleepingComputer
Mozilla, Google, Apple block compromised eMudhra CA certificates
BleepingComputer7:46 PM

Certificate authority eMudhra revoked eight compromised intermediate certificates after researchers found their private keys were so weak that anyone could recover them almost instantly and use them to forge trusted certificates for legitimate websites. [...]

r/netsec
France had more Internet-exposed Danfoss refrigeration dashboards than the rest of the world combined before the supermarket attacks (weekly IPv4 scan data)
r/netsec4:04 PM

I work at IPinfo, which runs a weekly scan of the IPv4 Internet. Short version of what we found: October 6–7 scan, five days before the attack: 2,528 addresses serving a Danfoss StoreView dashboard in 73 countries and territories. France had 1,331 (53%). 85% of the French ones ran software with known flaws, including 527 end-of-life AK-SM 800 units. Only 195 had every fix. Elsewhere it was 84%…

r/netsec
CVE-2026-46633: Proving exploitability of Twig sandbox bypass
r/netsec3:08 PM

I continued researching sandbox bypasses discovered in Twig by project Glasswing. This time, I focused on CVE-2026-46633, which still had no public exploits. This writeup documents my development of payloads for the CVE-2026-46633 and the corresponding SSTImap modules.

BleepingComputer
Zeabur shutting down after second security breach in two months
BleepingComputer2:33 PM

Development platform Zeabur has disclosed details of a cybersecurity incident in which an attacker used leaked internal credentials stored in plaintext to compromise its infrastructure and steal over 3.2 million environment variable records and information for 321,810 accounts. [...]

Cyber Security News
eMudhra Certificate Authority Compromise Triggers Emergency Action Across Browsers
Cyber Security News1:14 PM

The private keys behind eight eMudhra intermediate certificate authority certificates have been compromised, prompting emergency blocks across major browsers and software platforms. The affected certificates chain to roots trusted by Mozilla, Microsoft, Apple, and Chrome, placing clients that still accept them at risk of trusting forged certificates. However, the public disclosures reviewed do…

Cyber Security News
Google Cloud Outage Knocks UK Banks, Websites and Court Systems Offline
Cyber Security News12:17 PM

A Google Cloud outage disrupted UK banks, business websites and court video links on Tuesday, October 20, after a power event hit its London infrastructure. Google later said most affected services had recovered, although a small number of customers still faced problems. The incident began around 07:08 BST in europe-west2, Google’s London cloud region. Google […] The post Google Cloud Outage…

The Hacker News
Eight eMudhra CA Keys Compromised, Triggering Emergency Fixes Across Browsers and Software
The Hacker News12:09 PM

The private keys of eight eMudhra intermediate certificate authority (CA) certificates are compromised, Mozilla and Google's Chrome Root Program confirms on October 20. An intermediate CA signs the certificates that websites present, so anyone holding one of these keys could issue a certificate for any website that a browser would accept. A researcher reported the

Cyber Security News
3 Ways Threat Intelligence Makes Life Easier for American SOC Analysts
Cyber Security News11:26 AM

October is Cybersecurity Awareness Month, a good time to rethink how SOC analysts detect and investigate threats, draw conclusions from the first three quarters of 2026, and see how exactly your daily workflows could be improved.  One important takeaway is that visibility into your company’s internal environment alone isn’t enough to ensure effective enterprise security […] The post 3 Ways Threat…

The Hacker News
Critical FortiSIEM Flaw Gets Public Exploit PoC for Unauthenticated Remote Code Execution
The Hacker News10:38 AM

Cybersecurity researchers have released a proof-of-concept (PoC) exploit for a recently patched critical security flaw impacting Fortinet FortiSIEM that could result in arbitrary code execution. The vulnerability, tracked as CVE-2026-106173 (CVSS score: 9.4), is a critical path traversal flaw that could allow an unauthenticated attacker to execute unauthorized code or commands via specially

The Hacker News
Qilin and INC Ransomware Groups Exploit Palo Alto Networks Flaw to Bypass MFA
The Hacker News10:32 AM

Palo Alto Networks has disclosed that it's continuing to observe exploitation of a now-patched security flaw impacting  PAN-OS and Prisma Access by ransomware actors. The activity relates to CVE-2026-0257 (CVSS score: 7.8), an authentication bypass flaw that could be exploited by bad actors to set up unauthorized VPN connections. It was patched by Palo Alto Networks in May 2026 and was

Cyber Security News
FBI Suspects Cybersecurity Executive Helped ShinyHunters Run Extortion Website
Cyber Security News10:09 AM

Federal investigators suspect an executive at a United States consulting firm helped ShinyHunters operate a website used to pressure hacked companies into paying ransom demands. The allegation raises questions about whether trusted ransomware advisers crossed from helping victims into supporting the criminals demanding payment for stolen data. The suspected website operator has not been publicly…

Cyber Security News
Hackers Exploit Open Banking Services to Test Stolen Credentials Without Paying a Cent
Cyber Security News9:22 AM

Criminals have found a way to use open banking as a low-cost checking service for stolen bank and card details. In a campaign described by Group-IB, fraudsters abused a spend-management platform’s account-linking process to check whether credentials worked and whether linked accounts held funds. The platform did not lose money through stolen funds, but it […] The post Hackers Exploit Open Banking…

r/netsec
Free real-time Certificate Transparency stream, no API key
r/netsec9:14 AM

I put up a free public CertStream endpoint for anyone monitoring phishing or lookalike domains wss://api.certstream.dev/ No API key or signup needed, just connect over WebSocket Python example: https://certstream.dev/free-certstream-api.html Open source: https://github.com/reloading01/certstream-server-rust

The Hacker News
Hackers Use Autonomous AI Agents to Breach Company Websites, Target Over 1,200 Sites
The Hacker News9:07 AM

A Chinese-speaking criminal pointed autonomous AI agents at company websites and let them break in with almost no help, and a security researcher watched it happen because the operators left their control panels open on the internet. The agents tried more than 1,200 sites and reached websites belonging to more than 100 companies, including farm-equipment maker Deere, appliance company

Cyber Security News
WP2Shell Attack Lets Hackers Create WordPress Admin Accounts and Install Web Shells Without Login
Cyber Security News8:54 AM

WP2Shell combines two WordPress Core flaws to move from an unauthenticated request to server-side code execution. It can let an attacker create an administrator account and install a plugin-based web shell. Seqrite’s October 16 analysis lists affected releases, but does not establish widespread live exploitation. The report says the flaws were disclosed in July 2026. […] The post WP2Shell Attack…

BleepingComputer
CJIS v6.1 Compliance: 5 Practical Priorities for Agencies
BleepingComputer8:51 AM

CJIS v6.1 requires agencies to maintain strong authentication, account security, and audit controls while demonstrating ongoing compliance. Specops outlines five practical priorities covering MFA, account management, passwords, logging, and audit readiness. [...]

r/netsec
How I got over 300 Tor exit nodes removed
r/netsec8:33 AM

Author here :) TLDR: on Oct 2, 333 exits (~10% of Tor exits) started redirecting port 22 to 12 interception servers running a paramiko-based MITM that stole passwords and tried to drop Ebury on the target.

Cyber Security News
Hackers Use Generative AI to Build Custom Malware and Bypass Traditional Security Detection
Cyber Security News8:32 AM

Hackers are using generative AI to build custom malware, rewrite harmful scripts, and make phishing messages harder to spot. The shift puts pressure on security tools that mainly depend on known file signatures, while helping ransomware operators move faster from their first foothold to data theft and encryption. The danger is not that every AI-generated […] The post Hackers Use Generative AI to…

Cyber Security News
Thousands of Android Phones Ship With Hidden Malware That Disables Google Play Protections
Cyber Security News8:15 AM

Thousands of Android phones across more than 150 countries have been found running malware planted in their firmware before purchase. The campaign, called Midnight Mimosa, targets low-cost devices and gives attackers system access without requiring owners to download a harmful app or click a suspicious link. The malware can secretly install and remove apps, load […] The post Thousands of Android…

The Hacker News
Pegasus Spyware Infection Confirmed on Serbian University Rector's iPhone Days Before Election
The Hacker News7:59 AM

The iPhone of Vladan Đokić, rector of the University of Belgrade and a prominent supporter of Serbia's student protest movement, was infected with NSO Group's Pegasus spyware in 2026, the Citizen Lab said on October 19. The finding came six days before Serbia's October 25 snap parliamentary election. The infection used a zero-click exploit, meaning Đokić did not have to tap a link or

Cyber Security News
Hackers Hijack 790 GitHub Repositories to Steal Cloud Credentials and AI API Keys
Cyber Security News7:02 AM

A campaign called GhostAction has placed malicious GitHub Actions workflows in 790 repositories, putting cloud credentials, software-publishing tokens, and AI service keys at risk. The total is OpenSourceMalware’s count of publicly recoverable, validated repositories through October 9, 2026; it is not a claim that every repository leaked credentials or suffered confirmed misuse. The campaign…

The Hacker News
WhatsApp Hid Instructions in Help Pages Telling Its AI Chatbot Not to Recommend Privacy Regulators
The Hacker News6:41 AM

WhatsApp's help pages carried hidden instructions for its support chatbot that told it not to recommend a data protection authority or regulator to users who could no longer delete their accounts, even though WhatsApp's own privacy policy for Europe tells users they can complain to one. The text sat in the pages' code, never shown on screen, until it was removed by October 18. Whether the

Cyber Security News
Revolut Outage Disrupts Payments and Banking Services as Google Cloud Reports London Issues
Cyber Security News6:37 AM

Revolut suffered a major service outage on Tuesday, October 20, 2026, disrupting payments, cash withdrawals, and access to its banking app. The digital bank said customer money and data remained safe while engineers worked to restore affected services. The disruption came as Google Cloud reported problems in its London region. Reuters reported that a person […] The post Revolut Outage Disrupts…

The Hacker News
What Security Teams Can Do To Tame Wild Code
The Hacker News6:33 AM

A sales manager builds an AI-assisted workflow to route leads. It connects to customer records, summarizes inbound requests, and posts updates to a shared channel. The workflow saves time, reduces manual work, and soon becomes part of the team’s daily routine. Across the same organization, employees are building useful apps, agents, and automations faster than existing processes can support them

The Hacker News
Go Issues Emergency Update Blocking Eight CA Keys Over Undisclosed Security Concerns
The Hacker News6:32 AM

Go 1.27.3 and Go 1.26.10, released on October 20, make Go's certificate verifier reject any certificate chain that passes through one of eight intermediate certificate authority keys. Programs built on the new release will refuse connections to sites and services whose certificates were issued under those keys. The Go team says the keys belong to one certificate authority it has not

Cyber Security News
Hackers Target South Korean Banks With AI, Then Accidentally Expose Their Own Attack Tools
Cyber Security News6:09 AM

Hackers linked to AI-assisted attacks on South Korean banks left parts of their own infrastructure open, giving researchers a view of their tools and preparations. The exposed files showed a wider operation involving cryptocurrency theft tools, Linux attacks, and mobile security testing beyond the banking campaign. Public reporting cited in the investigation said the breaches […] The post Hackers…

The Hacker News
Russian APT28 Breaches NATO Naval Shipbuilder in NATO Country, Deploys New Reflective Loader
The Hacker News6:06 AM

The Russia-linked state-sponsored threat actor tracked as APT28 (aka BlueDelta, Fancy Bear, and Forest Blizzard) has been attributed to attacks targeting two member states of the North Atlantic Treaty Organization (NATO). The Symantec Threat Hunter Team, which is tracking the activity cluster under the moniker Swallowtail, involved the use of a backdoor called HOOKEDGE and a previously

Schneier on Security
Possible new Cellebrite iPhone Radio Zero-Day
Schneier on Security6:03 AM

Justin.sh is reporting on a confidential Cellebrite document that has been leaked to him: Cellebrite calls it Advanced Unlocks (AU from here on), not to be confused with the “advanced unlocking services” they’ve marketed for years. A press release from earlier this year confirms AU is a new product for 2026. […] According to Cellebrite, AU: is a “next-generation AFU vector that is more resilient…

The Hacker News
ConnectWise Resets Credentials as Cloud Backup Remains Offline After Security Incident
The Hacker News5:56 AM

ConnectWise on Monday said it has taken remediation measures, including strengthening administrative-access protections and resetting accounts and replacing application credentials, as it continues to respond to a security incident that led to unauthorized access to application identities associated with Cloud Backup. The company said it has completed the following actions since it began

Cyber Security News
ThreatBook Launches RedAgents AI Platform That Uses Multiple Hacking Agents to Find Security Flaws
Cyber Security News5:41 AM

ThreatBook has launched RedAgents, a cloud platform that brings several AI-powered penetration-testing agents together to assess an organization’s systems. Announced on October 16, 2026, the service is designed to help security teams find weaknesses in their own networks by running multiple automated tests within a defined, authorized scope. ThreatBook says the agents can work in […] The post…

Cyber Security News
U.S. Government Bans DeepSeek AI and Orders Federal Agencies to Remove All Related Tools
Cyber Security News5:18 AM

The U.S. Department of Homeland Security has ordered federal civilian agencies to stop buying DeepSeek products and remove related technology from their IT systems. The action covers products from Hangzhou DeepSeek Artificial Intelligence Co., Ltd., its affiliates, and third-party products and services developed using DeepSeek implementations. The notice was filed for public inspection on October…

Cyber Security News
Hackers Exploit Palo Alto VPN Flaw to Bypass MFA and Steal Credentials From VMware Disks
Cyber Security News5:03 AM

Ransomware operators are exploiting a Palo Alto Networks GlobalProtect VPN flaw to bypass multi-factor authentication and enter corporate networks. In one investigated case, attackers reached VMware management systems and stole credentials directly from a domain controller’s virtual disk, avoiding security tools running inside the virtual machine. Palo Alto Networks Unit 42 detailed the activity…

Cyber Security News
Hackers Hijack OVHcloud GitHub Releases to Distribute Secret-Stealing Malware
Cyber Security News4:16 AM

Hackers compromised the GitHub account of an OVHcloud developer and used it to distribute malicious files through the company’s official command-line tool releases. The October 19, 2026, supply chain attack targeted users downloading the OVHcloud CLI, with malware designed to collect secrets stored on their computers. A customer spotted suspicious release changes and alerted the […] The post…

Cyber Security News
Hackers Hijack AOMEI Software Updates for Just 5 Minutes to Secretly Install Backdoors
Cyber Security News3:59 AM

A short-lived change to AOMEI’s software update system gave hackers a way to deliver malware through a trusted route. Google Threat Intelligence Group (GTIG) and Mandiant found that attackers repeatedly altered AOMEI’s update settings for only a few minutes at a time between April and July 2026. Any AOMEI Backupper computer checking for updates during […] The post Hackers Hijack AOMEI Software…

The Hacker News
Hackers Hijack Five OVHcloud CLI Releases to Distribute Secret-Stealing Malware
The Hacker News3:21 AM

An attacker used a contributor's GitHub account to replace the download archives on five existing releases of OVHcloud's command-line tool on Monday, October 19. The account had been hijacked, and the new files were a build designed to steal secrets stored on the disk of any machine that runs it, the cloud provider says. They were live on GitHub for up to 94 minutes, from 12:47 to 14:21 UTC,

Cyber Security News
Hackers Compromise Rank Math PRO WordPress Plugin to Install Self-Rebuilding Backdoors
Cyber Security News3:20 AM

Hackers planted malware in copies of the Rank Math PRO WordPress plugin, exposing websites to hidden backdoors that can rebuild themselves after removal. Rank Math confirmed that some version 3.0.123 packages distributed during a limited October download window contained malicious code that could compromise websites when activated. The company removed the affected files and released […] The post…

Cyber Security News
Hackers Using Fake Google Meet Pages to Steal Google Credentials
Cyber Security News2:18 AM

Two websites are hosting fake Google Meet pages designed to steal Google account credentials and carry out phishing involving two-factor authentication (2FA), according to threat intelligence shared on October 20, 2026. The pages imitate a familiar meeting service to make a request for account details look more believable. The researcher also reported a serious security […] The post Hackers Using…

The Hacker News
ClickFix Attackers Exploit Siemens Software Center Flaw to Deploy Remote Access Trojan
The Hacker News2:11 AM

Siemens has addressed a DLL sideloading vulnerability impacting Siemens Software Center that it said has been exploited in ClickFix attacks. The high-severity vulnerability, tracked as CVE-2026-110936 (CVSS v4 score: 8.4), could allow an attacker to place a specially-crafted DLL in a directory the application searches, resulting in execution of malicious code with the same privileges as the

The Hacker News
Ex-OpenAI Engineer Detained in Spy Device Case as Saudi Royal Contacts Emerge
The Hacker News12:53 AM

A U.S. court on Monday granted the U.S. government's request to detain a former OpenAI engineer accused of planting a recording device in an executive conference room at the company's San Francisco office to allegedly steal sensitive secrets. In a new court filing Sunday, prosecutors revealed that Abdulrahman Alfozan, a 35-year-old Saudi national, was "in frequent communications via WhatsApp

Monday, October 19

Cyber Security News
SBI Data Breach Claim – Hackers Allegedly Claim Access to 3.75 Lakh Users’ Database
Cyber Security News11:40 PM

An unverified SBI data breach claim alleges that a threat actor named Siriusim posted customer records and banking documents online. The claimed dataset contains 375,000 CSV rows and 2,722 PDF files, but those figures do not establish that 3.75 lakh unique customers were affected. CyberPulse reported the allegation on October 16, 2026. Its post described personal customer […] The post SBI Data…

The Hacker News
Hackers Use New ROMULUS ClickFix Platform to Deliver LegionLoader and Other Malware
The Hacker News11:05 PM

Cybersecurity researchers have disclosed details of a ClickFix delivery platform called ROMULUS that's being used to distribute malware such as Legion Loader. According to Forescout Research - Vedere Labs, ROMULUS is akin to a malware delivery service that employs ClickFix-style lures on bogus landing pages to trick unsuspecting users into running malicious commands and infecting their own

Cyber Security News
One Hacker Uses AI Agents to Breach Over 100 Company Websites for Just $5,000
Cyber Security News10:43 PM

A Chinese-speaking hacker used AI agents to break into more than 100 company websites while spending an estimated $5,000 on AI tokens, according to a Reuters investigation in October. The operation shows how one person can direct software to carry out complex attacks with little ongoing human input. The targets included sites linked to Deere, […] The post One Hacker Uses AI Agents to Breach Over…

Cyber Security News
Claude AI Detects Hidden Crypto Miner While Building Temperature Monitor App on Mac
Cyber Security News9:49 PM

An ordinary coding task led to an unexpected security discovery when Claude Code reportedly found a hidden cryptocurrency miner on a developer’s Mac. The AI assistant was building a temperature monitoring app when unusually high sensor readings prompted it to investigate CPU activity. It identified XMRig consuming about 1,175% CPU, described as roughly 12 cores […] The post Claude AI Detects…

BleepingComputer
Hackers hijack AOMEI update servers to secretly spread malware
BleepingComputer2:40 PM

Hackers reportedly compromised AOMEI's servers to distribute malware through a built-in promotional feature in its backup software, briefly tampering with configuration files before restoring them to their original state to hide the attacks.a [...]

Cyber Security News
Critical Drupal RCE Vulnerability Could Let Attackers Take Over Websites Without Authentication
Cyber Security News1:13 PM

Drupal has released security updates for a critical remote code execution vulnerability that could let attackers take over affected websites without logging in. Tracked as CVE-2026-108097, the flaw affects the Field UI module in Drupal core. The Drupal Security Team published its warning on October 14, 2026. The official security advisory, SA-CORE-2026-014, assigns the issue […] The post Critical…

Cyber Security News
Microsoft Says AI Agents Cannot Be Trusted and Could Become Insider Security Threats
Cyber Security News1:04 PM

Microsoft warns organizations to treat AI agents as potential insider risks not because they are automatically malicious, but because they can access company data, apps, and tools and act on that access at high speed. The warning, published on October 19, 2026, comes as businesses use agents to handle tasks such as writing code, reviewing […] The post Microsoft Says AI Agents Cannot Be Trusted…

The Hacker News
Hackers Exploit Plex2Shell Flaws to Install Crypto Miners and Linux Proxy Backdoor
The Hacker News12:32 PM

Threat actors have begun to exploit a chain of vulnerabilities in Plex Media Server to deploy cryptocurrency miners and reverse proxy software, a day after a proof-of-concept (PoC) went public. According to a researcher who goes by the online alias boredhackerblog, the exploitation activity involves chaining four different vulnerabilities, collectively called Plex2Shell. The vulnerabilities

Cyber Security News
Bright Security Introduces STAR Fuzzer, Agentic Fuzzing That Writes Its Own Harnesses and Proves Every Finding
Cyber Security News12:11 PM

San Rafael, United States, October 19th, 2026, CyberNewswire Built on an evolutionary engine first released in 2018, STAR Fuzzer by Bright Security finds crashes, memory exhaustion and memory-safety bugs in security-critical code without a running application. In its first open source research run, it found High or Critical issues in 45% of the projects tested, […] The post Bright Security…

The Hacker News
Popular WordPress SEO Plugin Rank Math PRO Hijacked to Deliver Self-Restoring Backdoor
The Hacker News11:28 AM

Copies of Rank Math PRO, the paid version of the Rank Math SEO plugin for WordPress, that were downloaded from rankmath.com or delivered as updates between 20:02 UTC on October 15 and 07:12 UTC on October 16 contained malware, Rank Math said in a security notice published on October 16. Any site that installed and activated one of those copies should be treated as compromised, and the

Dark Reading
OnlyFans Copyright Takedowns Expose Compromised Websites
Dark Reading9:28 AM

Copyright takedown requests tied to OnlyFans and other adult content creators are revealing how attackers exploit vulnerable university and government websites to manipulate search results. UpGuard's Greg Pollock explains what universities, government websites, and security teams need to think about next.

The Hacker News
⚡ Weekly Recap: 98 Zero-Days, Rogue AI Agents, $100M Crypto Theft, 700 Supermarkets Hit and More
The Hacker News9:14 AM

The worst problems don't always come with a warning. Sometimes they arrive through a service everyone trusts, a device someone bought, or a system nobody thought to check. By the time something looks wrong, the damage may already be done. This week had plenty of that. Trusted connections became a problem. Hardware wasn't as safe as it looked. Old bugs found new victims, and some systems were

BleepingComputer
Inside the Underground Market for Know Your Client Services
BleepingComputer9:00 AM

Cybercriminals are selling forged identity documents, deepfake videos, and live verification services to help buyers bypass Know Your Client (KYC) checks. Flare examines how these underground services operate and the techniques used to create and maintain fraudulent verified accounts. [...]

r/netsec
An attack that corrupts a LLM model about one specific fact - no file changes, no process, no network. Nothing to scan, and you can still detect.
r/netsec8:53 AM

Think about what a model does: it answers questions correctly, you trust it, you wire it into things. Now imagine it’s correct about everything except one topic you care about, and it’s wrong about that on purpose. A dosage. A legal fact. A person. A “is this config safe to deploy.” The other 99.9% is pristine, so nobody looks twice. The attack that does this doesn’t touch disk. The checkpoint…

Krebs on Security
Feds Suspect Ransom Negotiator Ran ShinyHunters Extortion Site
Krebs on Security8:48 AM

U.S. federal investigators pursuing the ShinyHunters hacking group that recently stole highly sensitive data from the FBI have identified executives at two different ransomware negotiation firms who maintained unusually close relations with the extortion group, KrebsOnSecurity has learned. Sources close to the investigation say one of the executives in the United States even helped ShinyHunters…

The Hacker News
GhostAction Attackers Plant Credential Stealer Disguised as Font in 94 GitHub Repositories
The Hacker News8:05 AM

The threat actor behind the GhostAction supply chain attack has expanded beyond injecting malicious GitHub Actions workflows into compromised projects to phish open-source developers and deliver a stealer malware disguised within a fake font file. The latest evolution, detailed by OpenSourceMalware, signals that the attackers are actively refining their modus operandi in response to steps

Cyber Security News
NSA, CISA and NIST Release New Security Guidelines to Detect and Shut Down Rogue AI Agents
Cyber Security News7:08 AM

NSA, CISA, and NIST have released joint security guidelines to help organizations detect, contain, and shut down AI agents that act beyond their approved tasks. Published October 16, 2026, the voluntary guidance sets out ten practices for managing incidents during superintelligence training and evaluation, with a focus on maintaining human oversight. The NIST announcement groups […] The post NSA…

Cyber Security News
Hackers Exploit SiteGuard WAF Vulnerability That Could Give Them Full Control of Servers
Cyber Security News7:07 AM

Hackers are exploiting a command injection flaw in SiteGuard Server Edition, a web application firewall installed directly on protected servers. Tracked as CVE-2026-106931, the vulnerability could let attackers run operating system commands with root or SYSTEM privileges, potentially giving them full control of an affected server. The flaw affects the product’s statistics function, which is […]…

The Hacker News
From Email-to-Case to the Boardroom: How Inherited Agents Break Governance Built for Software
The Hacker News6:50 AM

In Salesforce Agentforce, the recommended way to make an agent respond to events is a Flow: a record is created or a case is updated, and the Flow passes data into the agent's prompt. Separately, Email-to-Case and Web-to-Case turn inbound customer messages into case records; it is how airlines and hotels run support intake. Both are standard, documented, as-designed features. Chained together,

Cyber Security News
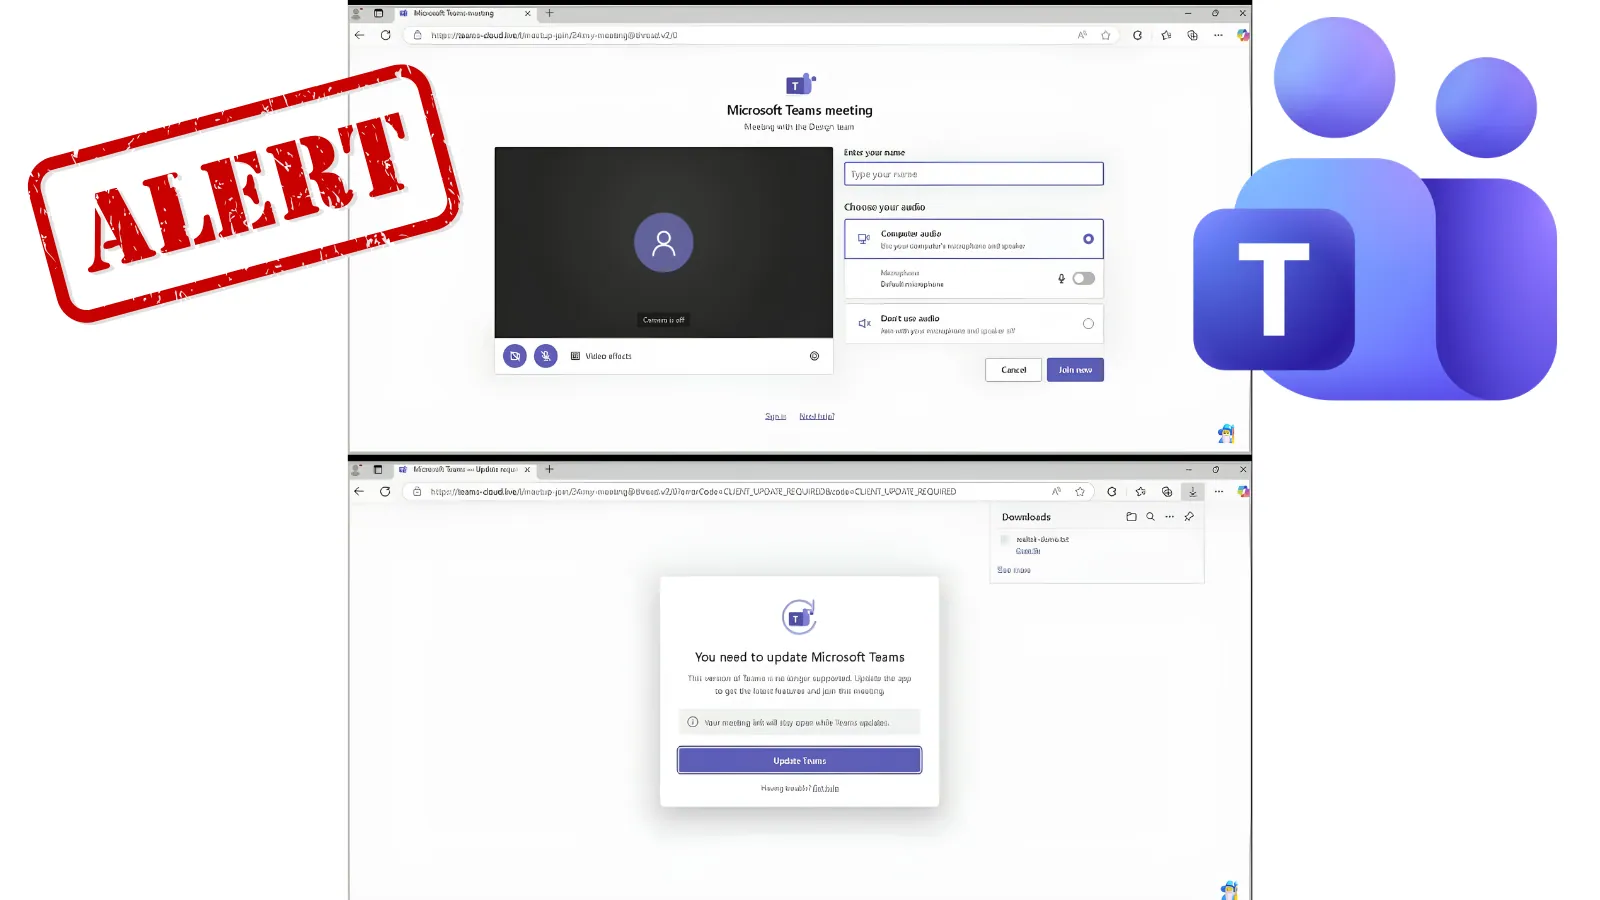
Hackers Registered New Teams-Based Domains and Used a Login Page to Steal Your Logins
Cyber Security News6:40 AM

A newly registered domain copies Microsoft Teams’ login page and interface, raising concerns about a phishing attempt targeting workplace users. Security researcher Steven Lim reported that teams-cloud[.]live was just five days old when he flagged it on October 18, 2026. He urged organizations to block the address before employees encounter the fake site. The alert […] The post Hackers Registered…

Cyber Security News
16-Year-Old Broadcom Wi-Fi Flaw Lets Attackers Hack Routers Without Knowing Passwords
Cyber Security News6:36 AM

A 16-year-old flaw in Broadcom’s Wi-Fi software can let attackers within wireless range take control of affected routers without knowing the network password. Security researcher Quentin Kaiser disclosed the issue at Hexacon in Paris on October 16, 2026, warning that old code remains in widely deployed devices. According to Kaiser’s research, the flaw has existed […] The post 16-Year-Old Broadcom…

Schneier on Security
Training AIs to Solve CAPTCHAs
Schneier on Security6:07 AM

Interesting research : Abstract : Vision-language models (VLMs) can solve visual CAPTCHAs without task-specific training, but the agents built on them approach every challenge from scratch. For such an agent, the hundredth instance of a familiar puzzle costs as much time and compute as the first. Specialized detectors invert the trade-off, answering in milliseconds but only for categories they…

The Hacker News
Fake Web3 Accelerator Uses npm Packages to Spread Malware and Hijack AI Agent Traffic
The Hacker News5:06 AM

A fake Web3 accelerator has been observed pushing information stealers and backdoors to Windows and macOS systems using malicious npm packages under the pretext of offering free artificial intelligence (AI) credits for Anthropic Claude and Google Gemini, coding tools, and security audits. "The tools delivered information-stealing malware and backdoors for macOS and Windows machines," Elastic

Security Magazine
You Asked. Now Ask Again.
Security Magazine4:00 AM

Good leadership often hinges on asking good questions. My journalism and media-training background particularly informs how I approach them.

The Hacker News
Unpatched Broadcom Wi-Fi Flaw Lets Attackers in Range Run Code as Root on Routers
The Hacker News1:29 AM

A flaw in Broadcom's Wi-Fi setup software lets an attacker within radio range run code as root on Broadcom-based routers, without the network password or any pairing step, security researcher Quentin Kaiser disclosed on October 16. He showed the attack working against home gateways supplied by three Belgian internet providers, in one case reading the Wi-Fi password off the device

The Hacker News
OpenCode Console Breach May Have Exposed OpenAI, Anthropic, and Google API Keys
The Hacker News1:07 AM

An intruder reached a legacy system at OpenCode on the night of October 16 and may have exposed the third-party AI provider keys that users had saved in OpenCode Console, the company said. Console is OpenCode's optional hosted service: a workspace saves its own OpenAI, Anthropic, or Google key there, and Console uses that key to call the provider so team members can use the models without

Cyber Security News
Google Unveils New Android AI Protections to Block Scam Calls, Phishing Links and OTP Theft
Cyber Security News1:04 AM

Google has announced a new set of Android security protections designed to stop mobile scams across calls, text messages, chat apps, web links, and account verification codes. The update comes as criminals increasingly use spoofed phone numbers, fake bank alerts, phishing pages, remote screen sharing, and AI-generated voices to trick users into giving up money […] The post Google Unveils New…

Sunday, October 18

Cyber Security News
Hackers Exploiting Plex Vulnerabilities in the Wild to Deploy Cryptominer Malware
Cyber Security News11:14 PM

Hackers are exploiting flaws in Plex Media Server to install cryptocurrency mining malware, with a researcher recording successful attacks against a honeypot on October 17, 2026. The activity follows the release of Plex2Shell, a public exploit that chains four vulnerabilities to run code without logging in. Later observations also revealed proxy software running alongside the […] The post Hackers…

Cyber Security News
Microsoft Confirms October Windows Updates Can Break Exchange Server Email Services
Cyber Security News10:39 PM

Microsoft has confirmed that Windows Server security updates released on October 13, 2026, can disrupt Exchange Server email services, blocking webmail access and leaving messages undelivered. The issue affects some on-premises systems running Exchange Server 2016, Exchange Server 2019, and Exchange Server Subscription Edition. Microsoft has published a workaround and advises administrators not…

r/cybersecurity
Mentorship Monday - Post All Career, Education and Job questions here!
r/cybersecurity7:00 PM

This is the weekly thread for career and education questions and advice. There are no stupid questions; so, what do you want to know about certs/degrees, job requirements, and any other general cybersecurity career questions? Ask away! Interested in what other people are asking, or think your question has been asked before? Have a look through prior weeks of content - though we're working on…

The Hacker News
ConnectWise Suspends Cloud Backup After Attackers Compromise Microsoft 365 Tenants
The Hacker News3:23 AM

ConnectWise on Saturday said it has disabled seven ConnectWise application identities as it continues its investigation into an incident in which unknown threat actors obtained unauthorized access to the application identities and compromised Microsoft 365 tenants. The disabled identities are listed below - ConnectWise Cloud Backup - 506e08f9-6e9a-4da4-942b-a099a03644ae ConnectWise